

Managing Environmental and Social Risks in Financing
Principles of Risk Management
MUFG has identified the risks associated with various environmental and social issues, and recognizes that they exert significant influence on the Group's corporate management for sustainable growth. As a financial institution that aims to be a trusted global financial group chosen by the world, the Group also grasps the risks caused by its business activities and endeavors to control and reduce them. MUFG manages these sustainability-related risks within the MUFG Environmental and Social Policy Framework, which is based on the MUFG Environmental Policy Statement and the MUFG Human Rights Policy Statement. The Framework is managed by the Sustainability Committee under the Executive Committee, and it is formed to be consistent with the framework for controlling reputational risks that could damage the Group's corporate value.
In addition, the status of policies and initiatives to the environmental and social risks are discussed and reported by the Credit & Investment Management Committee, the Credit Committee and the Risk Management Committee depending on the theme. Conclusions reached by the above committees are reported to the Executive Committee, and reported to and discussed by the Board of Directors, and the Board of Directors oversees risks related to environmental and social issues.
The application of this Framework remains subject to compliance with local laws and regulations.
Risk Assessment Process
Standard due diligence is conducted by departments that have direct contact with customers to identify and assess the environmental and social risks of business that is to be financed by MUFG. If it is determined that the business needs to be examined more carefully, MUFG conducts enhanced due diligence and decides whether or not to finance the business.
As for business that would have significant environmental and social risks and could potentially damage MUFG's corporate value or develop into a reputational risk, MUFG holds discussions on how to handle it within a framework participated by senior management. In addition, the Bank adopted the Equator Principles, a framework for identifying, assessing and controlling the environmental and social risks of large-scale projects, and conducts risk assessments in accordance with its Guidelines.
The process of identifying and assessing the environmental and social risks or impacts of a business to be financed

Major Risks and Responses
| Prohibited Transactions | Transactions of High Caution |
|---|---|
|
[Cross-sector guidelines]
[Sector specific guidelines]
|
Cyber Security
Basic Policy
Cyber Security Management Structure
Governance Structure
MUFG has established cyber security standards that refer to international guidelines and is engaged in the development of relevant strategies and organizational structures as well as the planning and implementation of initiatives aimed at enhancing its cyber security measures.
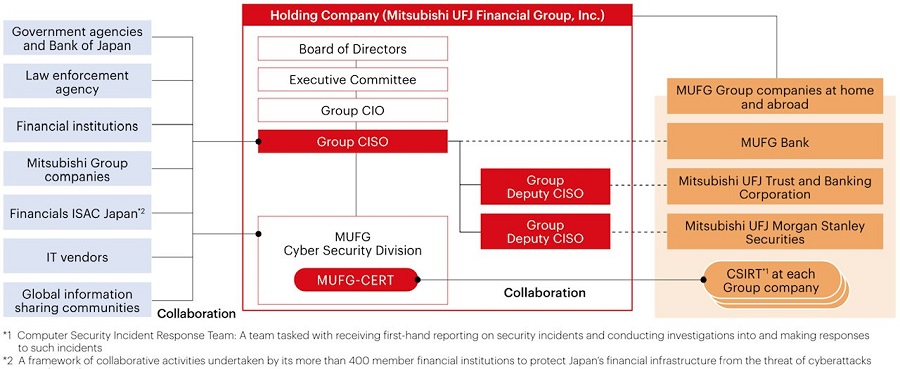
MUFG enacted the Cyber Security Management Declaration with the intention of strengthening the security management structure under the direct supervision of top management as a response to cyber-attacks and crimes that are becoming more advanced and sophisticated year by year. Moreover, in 2022, MUFG separated the Cyber Security Office from the Information Systems Planning Division as an independent division operating under the leadership of the Group Chief Information Security Officer (CISO). MUFG has a governance structure supporting business judgement according to changes in the surrounding environment through timely and appropriate reporting to the Board of Directors and other relevant committees at least twice a year. Taking advantage of the structure, MUFG puts effort into the effective and efficient promotion of cyber security strategies while continuously working to defend MUFG against day to day cyber-attacks.
Management Structure
- MUFG Cyber Security Fusion Center Office (MUFG CSFC)
Cyber Security Governance Structure (MUFG)
Main Initiatives to Counter Cyber Security Threats
Security Measures to Counter Growing Threats
MUFG has set up a dedicated team focused on threat intelligence to centralize such related activities as impact analysis for newly found vulnerabilities or past experiences, and remediation for those impacts on a groupwide and global basis. Additionally, the team monitors systems for external stakeholders daily to prevent any flaws in security updates or configuration settings.
In step with the widespread popularization of electronic payment via such internet services as Internet banking, cybercrimes that target online services have become a social issue. MUFG is implementing a variety of initiatives to deliver safe and secure services to customers, such as ensuring robust online verification, thoroughgoing vulnerability countermeasures, threat intelligence, anomaly detection and suspicious-transaction monitoring.
Furthermore, we have obtained external certifications such as PCI DSS (Payment Card Industry Data Security Standard) as needed, striving to enhance the reliability of our systems.
Cyberattacks are becoming increasingly sophisticated and complex as technology continues to advance, including the emergence of frontier AI. While MUFG continuously strengthens its cybersecurity measures, it is difficult to prevent all cyberattacks before they occur. To prepare for potential cyber incidents, MUFG has established response processes to ensure timely and effective escalation, information sharing with relevant external parties including regulators, decision-making, external communications with customers and other stakeholders, and technical response. MUFG also conducts regular exercises and training involving senior management and relevant departments to continuously strengthen its incident response capabilities.
Our Response to Digital Transformation (DX)
MUFG actively utilizes such new technologies as cloud services, AI, Robotics and Open APIs for business.
The Cyber Security Division participates in projects related to new technologies from the early stages, such as the planning and design phases. This activity contributes to the development of multilayered security measures and the realization of coexistence between safety and technology-driven transformation through proactive actions, including procedure development for the safe utilization of new technology, risk evaluation and the monitoring of configuration settings.
Nurturing Security Specialists
Cyber security measures cover a wide range of areas, including governance, threat intelligence, risk management, engineering, monitoring operation and incident response. MUFG has secured an in-house team capable of managing and carrying out the above functions.
To ensure the robust implementation of each security measure, MUFG has systematically categorized the talents and skill sets expected of security members to provide them with optimally designed human resource development programs, which combine in-house and external lectures and exercises while giving due consideration to the competencies of each member, the nature of tasks to be assigned to them and possible opportunities for their future career advancement. Furthermore, MUFG has boldly pursued the improvement of security measures in order to keep up with constant changes in technology, the utilization environment and cyber-attacks, and to nurture them in its professional capacity. Through these initiatives, MUFG’s cybersecurity professionals were recognized for their contributions across various areas of expertise, and MUFG received the FY2024 Annual Award from Financial ISAC Japan(note) in May 2025.
- A framework of collaborative activities undertaken by its more than 400 members financial institutions to protect Japan’s financial infrastructure from the threat of cyberattacks
Providing Cyber Security Education to Foster a Proper Culture
For MUFG to maintain the stable operation of its financial infrastructure, it is essential to foster the corporate culture in which each employee understands the importance of cyber security and considers what should be done as a company while acting in collaboration with other financial institutions or government authorities.
MUFG provides educational programs to not only employees directly involved in cyber security but also other employees within our group, including temporary and part-time staff, who are engaged in the planning and promotion of our services so that the whole employees are well-versed in necessary countermeasures against cyber-attacks. Furthermore, MUFG provides employees at main Group companies with e-learning, phishing mail exercises and newsletters for alerting readers of cyber-attacks and familiarizing them with proper responses. It also hosts seminars for a wide scope of Group companies. In addition, MUFG is engaged in various activities with external organizations, such as various training programs and drills hosted by the NISC (National center of Incident readiness and Strategy for Cybersecurity), the Financial Services Agency, and the Tokyo Metropolitan Police Department.
In July 2022, MUFG signed a partnership agreement involving industry-academia-government collaboration to help develop cybersecurity talent across society. Based on this agreement, MUFG will expand the scope of interactions with partners from different sectors and universities to enhance its own cyber security measures. At the same time, we convey MUFG’s insights to society, with the aim of contributing to the enhancement of cyber security measures for society as a whole.
Combating Financial Crime
Measures to Prevent customers from attacks by Bank Transfer Frauds
To prevent customers from falling victim to fraud, including bank transfer fraud and investment and romance scams conducted through social media, which have become increasingly common in Japan, we provide fraud alerts to customers through posters at ATM areas and messages displayed on ATM screens. In addition, we promote a campaign encouraging customers to refrain from phone calls while using ATMs, as mobile phones are often used by fraudsters to guide victims through transactions.
We also impose restrictions on certain ATM transactions for some customers where there is a risk of fraud.
Furthermore, through “Mitsubishi UFJ Direct,” we provide fraud prevention alerts when customers register for the service or increase their transaction limits. We also monitor money transfers and contact customers to verify transactions when suspicious activity is detected.
When customers request to withdraw large amounts of cash or transfer funds at our branches, our staff alert them to potential fraud and ask about the details and purpose of the transaction. We also work with the police when necessary to help prevent customers from falling victim to fraud.
Measures to Prevent Fraudulent Use of Bank Accounts
When customers open a new bank account, we verify their identity and confirm the purpose of opening the account. In addition, to prevent bank accounts from being misused for financial crime, we use leaflets, our website, and other channels to inform customers that selling, buying, transferring, or lending bank accounts (so-called “account rental”), including as part of fraudulent job offers, constitutes a crime.
We also continuously monitor accounts suspected of being misused and, when necessary, restrict transactions or suspend the use of such accounts to prevent them from being used for criminal purposes.
We also provide information on our website and through other channels on how customers can avoid becoming involved in such activities and what to do if they do become involved.
Measures to Prevent Loss from Counterfeit or Stolen ATM Cards
Security Measures for Internet Banking Service
A variety of security measures have been implemented to help prevent unauthorized access and fraudulent transactions by third parties through phishing or malware.
MUFG Bank (the Bank) and Mitsubishi UFJ Trust and Banking (the Trust Bank) have introduced an electronic authentication system, which displays a warning message if an email from the Bank or the Trust Bank has been tampered with. This system also allows customers to confirm that the server they access during Internet banking transactions is authentic.
For individual customers, the Bank and the Trust Bank provide authentication methods such as one-time passwords generated for single use, through their respective Internet banking services, “Mitsubishi UFJ Direct” (the Bank) and “Mitsubishi UFJ Trust Direct” (the Trust Bank).
We are also working to strengthen authentication. For example, the Bank provides “MUFG Anshin Pass,” a multi-factor authentication service designed to be resistant to phishing attacks, through “Mitsubishi UFJ Direct,” thereby reducing the risk of fraudulent transactions by third parties.
Mitsubishi UFJ Morgan Stanley Securities Co., Ltd. has implemented measures to reduce the risk of unauthorized access in accordance with relevant supervisory guidelines. For example, it requires passkey authentication when logging in to its online trading service and has adopted email authentication standards that enable the company’s authenticated logo to be displayed in its emails, thereby reducing the risk of unauthorized access and fraudulent transactions by third parties.
Security measures for corporate customers include the Internet services “BizSTATION” (the Bank) and “the Bank Business Direct” (the Trust Bank) and the provision of the “One-Time Password Card” (the Bank) and the “Transaction Authentication Token” (the Trust Bank).
Efforts to Detect Unauthorized Credit Card Use
Mitsubishi UFJ NICOS is committed to complying with the Payment Card Industry Data Security Standard (PCI DSS), an international security standard for the credit card industry, developed to ensure the safe handling of credit card membership data. We have obtained compliance certification for systems involving the credit card business and are striving to maintain and improve security.
To prevent customers from becoming involved in malicious credit card crimes, we have introduced a fraud detection system that uses AI and other technologies to monitor customers’ credit cards 24 hours a day, 365 days a year, for unauthorized use by third parties.
So that customers can use their credit cards with peace of mind, we may temporarily place suspicious transactions on hold and send email messages requesting confirmation, or confirm use by the cardholder through contact by telephone or Short Message Service (SMS) following the transaction. When use by a party other than the cardholder has been determined, to prevent damage from unauthorized use we carry out procedures to suspend use of the card in question and replace it with a new card bearing a different card number.
Acquisition of ISO / IEC27001 Certification
Acquired PrivacyMark (PMark) Licensed Operator Certification
(As of September 2026)